
Limited visibility
As infrastructure scales, it gets harder to get visibility needed to find and fix issues.
Attending KubeCon in Salt Lake City? Meet with the Spacelift team

IaC Orchestration that moves at AI speed
Provision, configure, and govern cloud infrastructure in one workflow
Poor visibility into what’s running, limited control over provisioning, and no centralized IaC pipelines slow you down
As infrastructure scales, it gets harder to get visibility needed to find and fix issues.

The more access developers need, the harder it is to enforce Golden Paths and catch rogue changes.

No self-service means developers wait on you for every deployment.
Provision, configure, and govern every IaC tool you run, in one workflow
Use Terraform, OpenTofu, CloudFormation, Pulumi, Kubernetes, Ansible, or Terragrunt, or just describe what you need. Your teams keep their tools, and Spacelift standardizes how they run.
Push code to your VCS system or ask the infrastructure assistant to generate, update, and open pull requests for you.
Provisioning is half the job. Spacelift configures resources in the same workflow, with shared contexts and credentials.
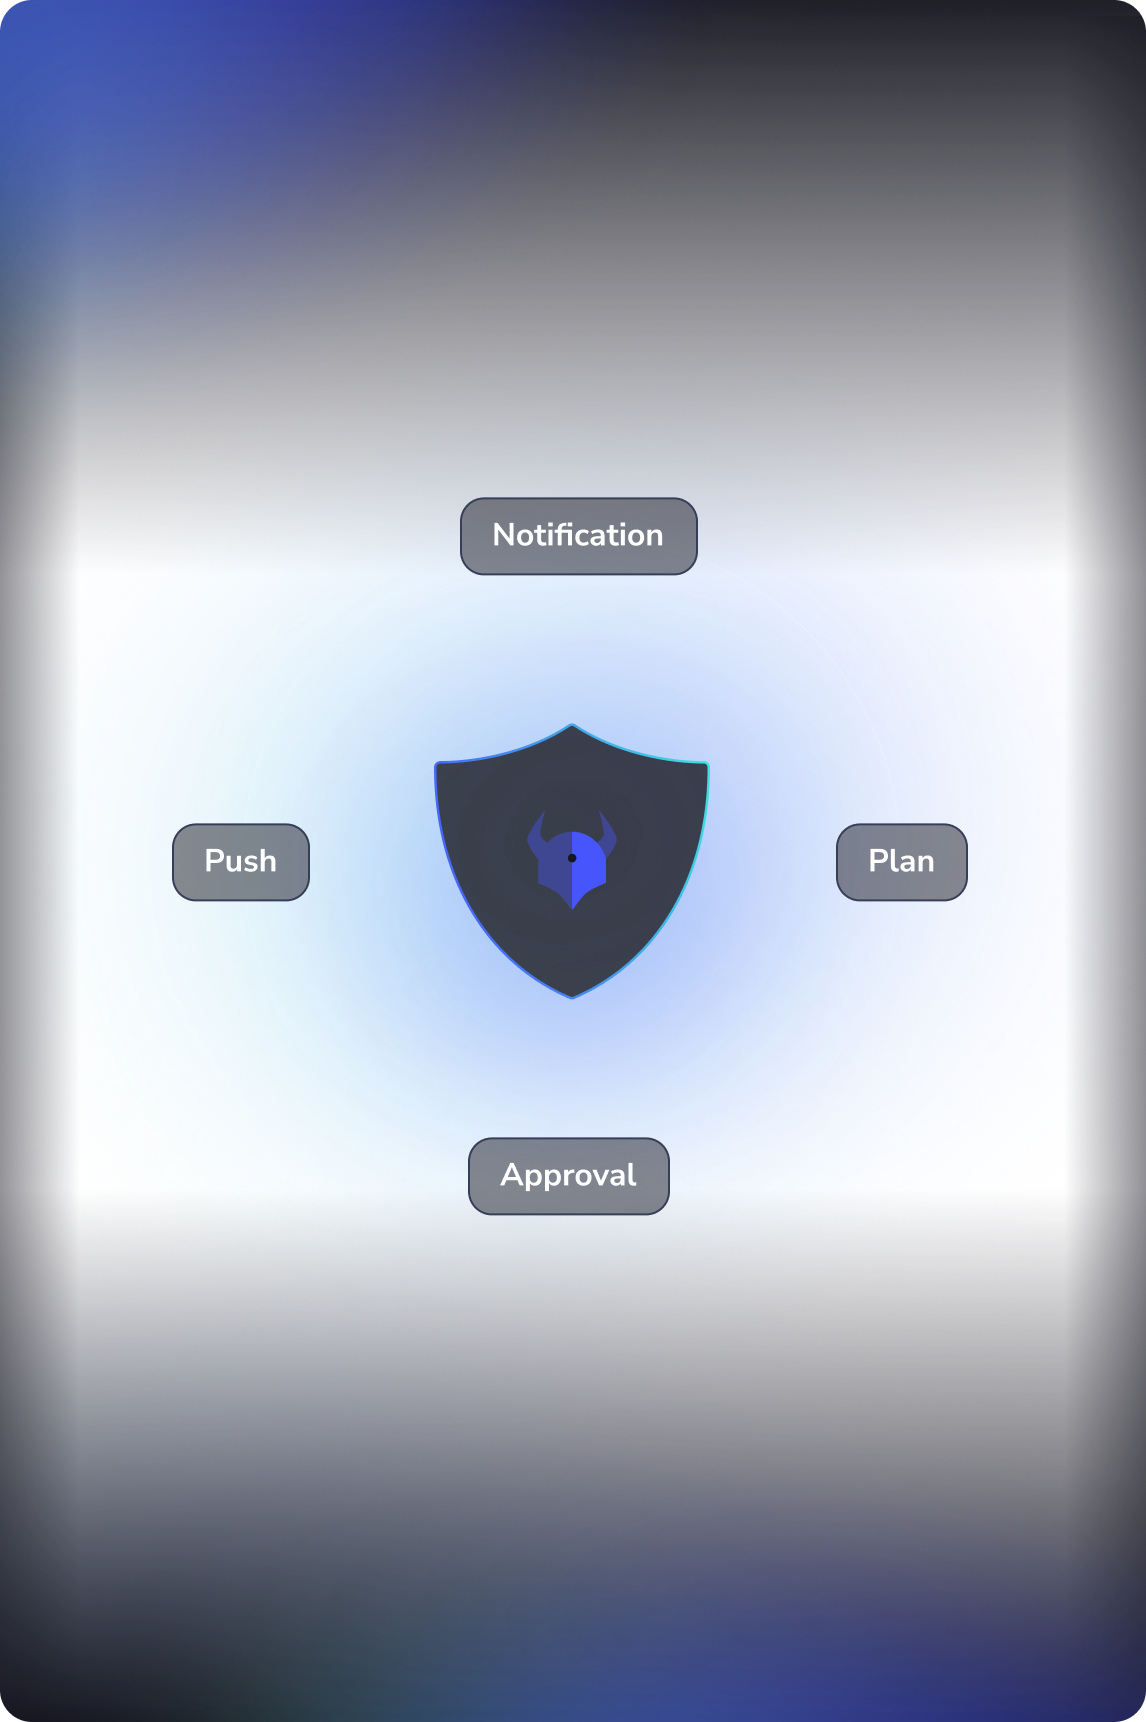
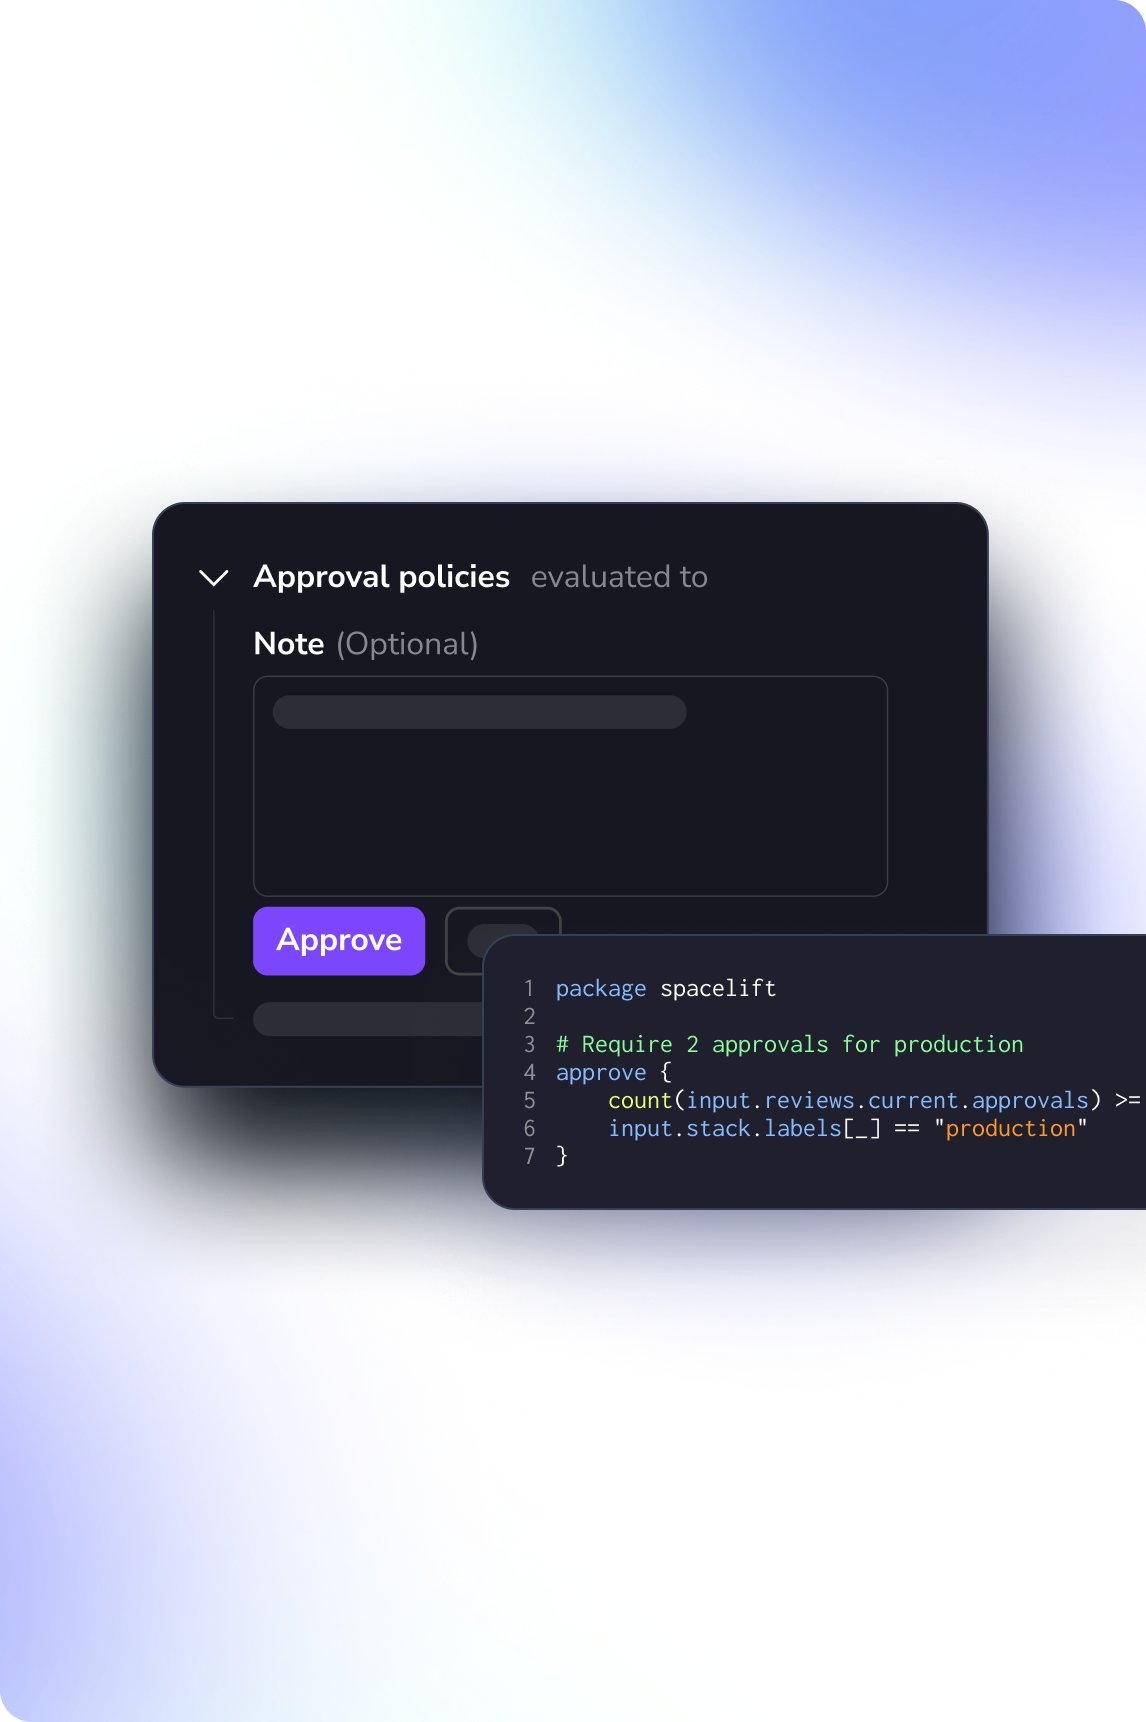
Embed plan, approval, and notification policies with OPA, or describe the guardrails you want and let the assistant generate the policy for you.
Run every deployment through a Git-driven, policy-enforced workflow built specifically for IaC and audited automatically.
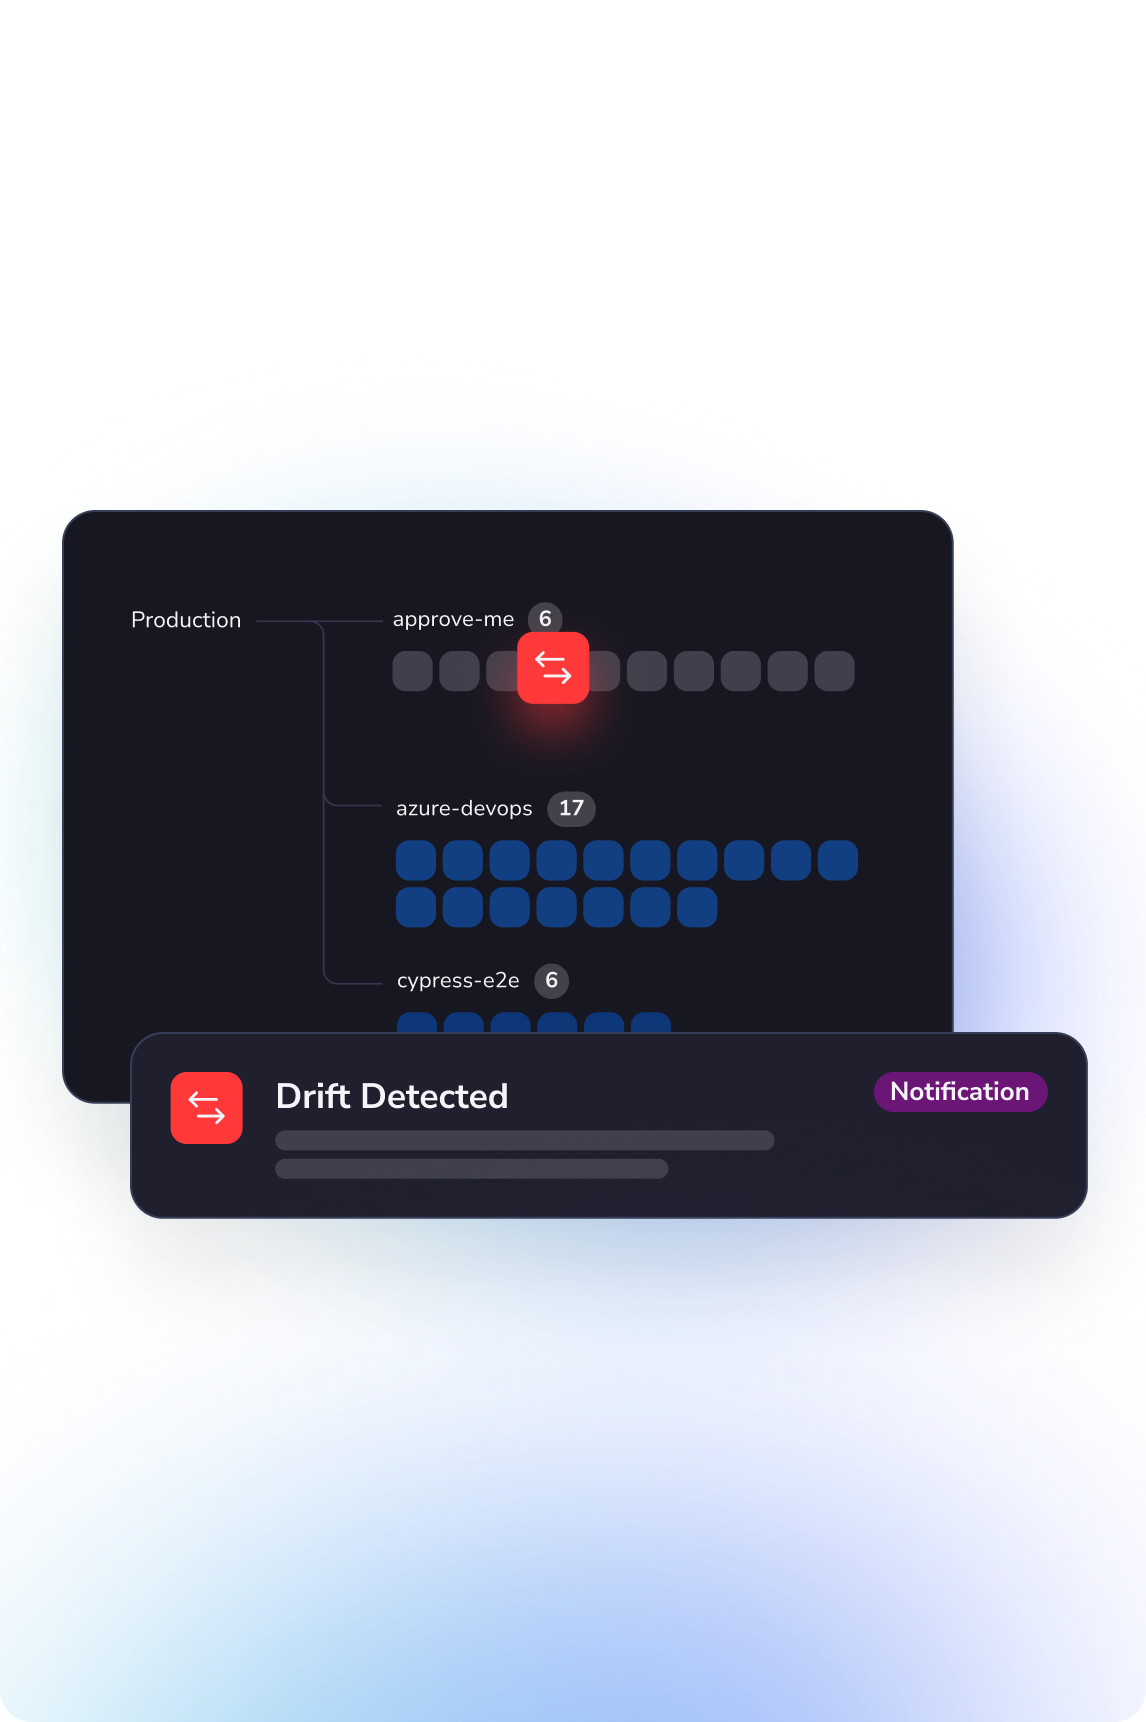
Spacelift continuously monitors your deployed resources and automatically detects when reality drifts from your desired state.
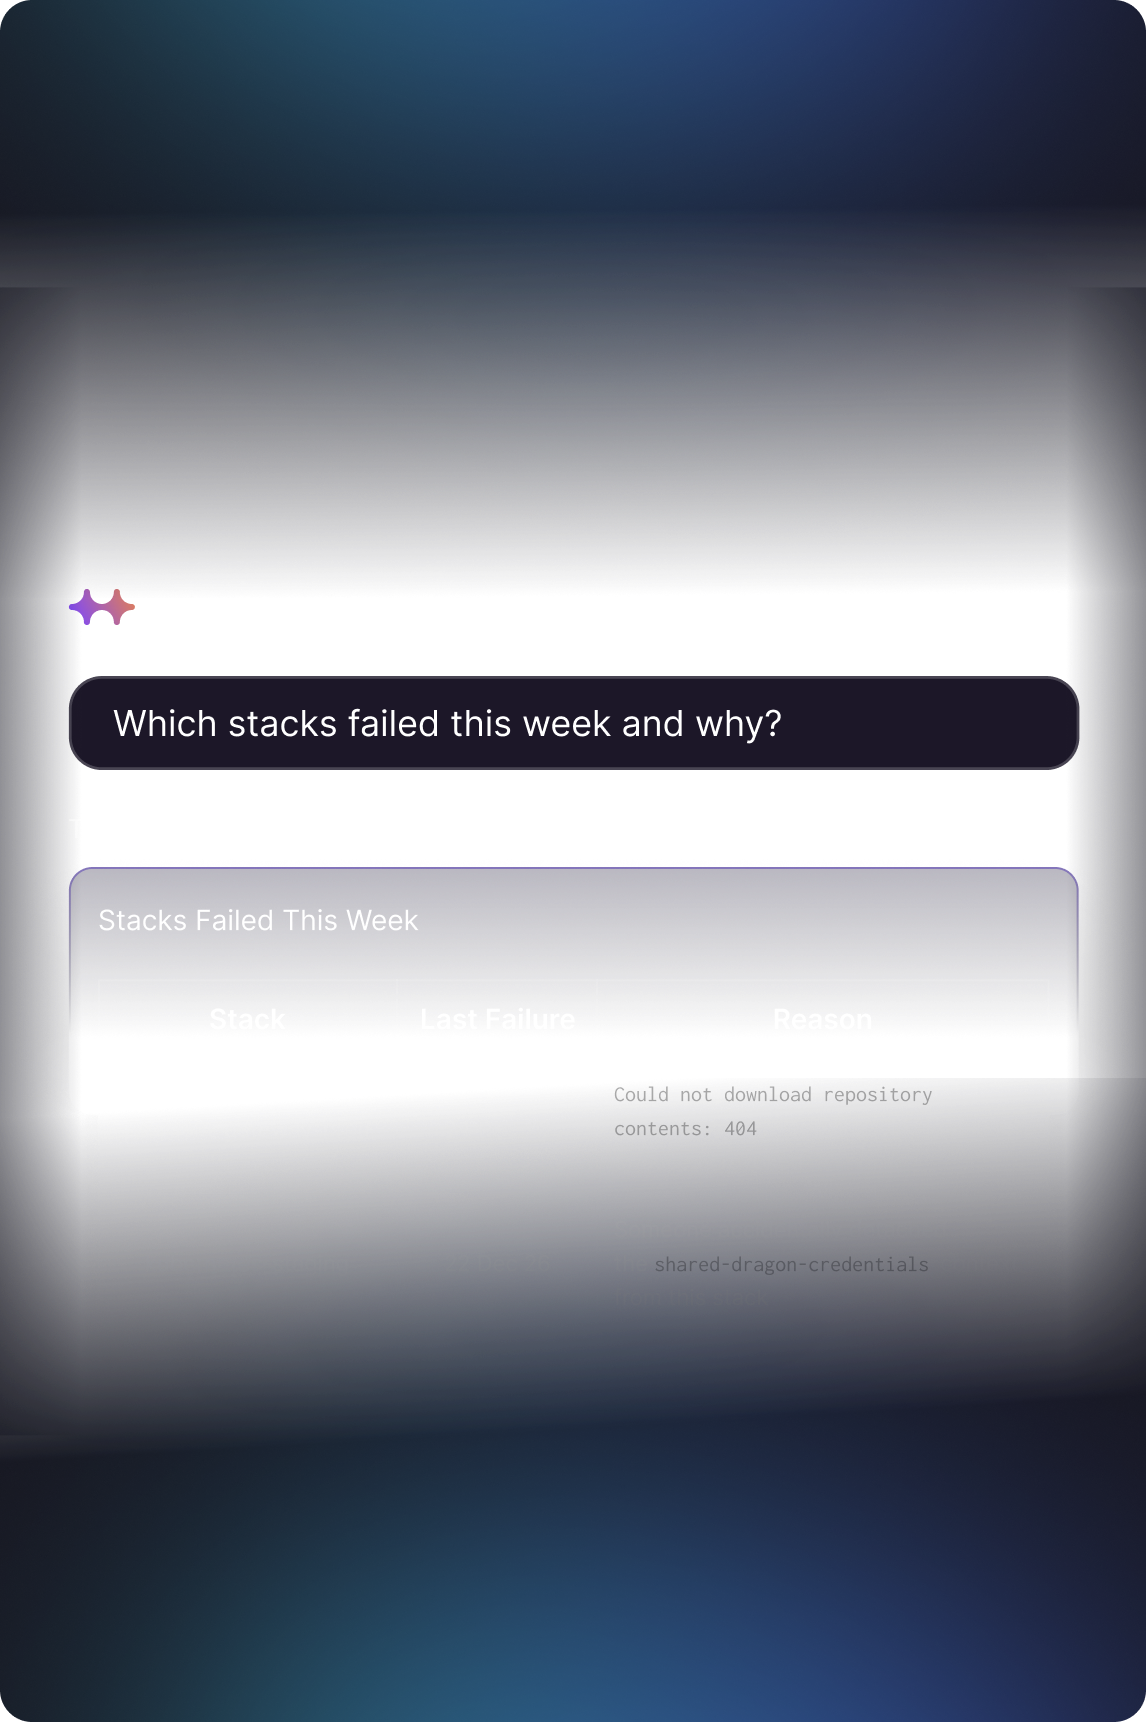
Ask the infrastructure assistant what’s deployed, what changed, or where you’re exposed, and get answers grounded in your actual stacks, state, and history.

Ship infrastructure in clean, isolated units that are easy to manage, scale, and own.

Coordinate complex, multi-environment deployments with relationships that define ordering and data flow between stacks.

Enforce security, compliance, and approvals with automated policy-as-code rules across runs and access events.

Protect your infrastructure state with secure, centralized storage and handling of Terraform and OpenTofu state files.

Define who can view, modify, or execute actions within Spacelift.

Share configuration, secrets, and standards across environments without duplicating effort.

Centralize authentication through an identity provider and eliminate credential sprawl.

Provision and authenticate securely across clouds using dynamic, short-lived credentials.


Connect to version control systems that trigger runs based on repository changes.

Let developers self-serve infrastructure with reusable templates that standardize and automate the creation of new stacks.

Segment teams, environments and processes with logical boundaries that organize stacks, access controls, and policies within an account.

Prove who changed what, when, and why with records of activity and system events for traceability and compliance.

A private registry for publishing and consuming reusable Terraform or OpenTofu modules.

Catch configuration drift automatically before it becomes a problem.

Connect helpful tools such as Checkov, Infracost, and Wiz directly into your workflows with a few clicks.
Provision and configure infrastructure in one workflow. The controls to manage risk and meet compliance are already built in.
Every deployment through your platform team is a queue. Give developers automated workflows, so they provision on their own.
Tooling built for one team and one cloud breaks as you scale. Spacelift connects every tool into one workflow.
Inconsistent practices mean more manual requests and audits. Spacelift gives you a single governed workflow for provisioning, configuration, and management.
Teams use Spacelift to shrink infrastructure provisioning lead times from days to minutes, cut down on drift and manual approvals, and finally get out of the ClickOps era.
See how Spacelift can turn your infrastructure provisioning from a ticket queue into a governed, self-service workflow your teams actually like using.